








An iGaming penetration testing specification should define the systems, identities, environments, methods, limits and evidence that an authorized tester may use before a platform or app is accepted for release. Buying a generic test does not answer whether player authentication, wallet commands, game sessions, administrator tools, integrations and recovery paths were actually exercised inside the agreed boundary.
For an operator CTO, security lead, compliance owner, product leader or procurement buyer, the decision is whether the engagement can find meaningful weaknesses without endangering live players or leaving the final release decision to a severity label alone. The useful delivery artifact is a versioned scope and rules-of-engagement pack linked to a findings register, remediation evidence and an independent retest record.
Separate the penetration test from scans and audits
An iGaming penetration test is an authorized attempt to validate whether weaknesses can be reached and combined across a defined technical scope. A vulnerability scan mainly identifies known patterns. A security audit evaluates controls and evidence against stated requirements. These activities can inform one another, but none is a substitute for the others.
The UK Gambling Commission’s security audit advice requires relevant remote licensees to undergo an independent annual audit against specified security requirements. Its evidence examples include reviews of externally conducted penetration testing and vulnerability assessments. That wording places test evidence inside a wider control review; it does not say that a penetration-test report alone completes the audit.
Define the purpose before selecting tools. A release test may validate a changed authentication journey, wallet integration or administrative role. An annual program may sample a broader set of trust boundaries. A supplier onboarding test may validate an exposed integration and the controls around vendor access. Record which decision the test supports and which decisions remain outside it.
Map critical systems and trust boundaries into scope
The penetration-test scope should follow sensitive data and authoritative actions across the complete service, not stop at the public website. List hosts, applications, APIs, mobile or web clients, administrator surfaces, identity services, wallet and payment boundaries, game or betting services, data stores, cloud resources, third-party connections and monitoring paths that the release can reach.
The Commission’s security-audit advice identifies critical systems that handle sensitive customer information, account balances, random-number generation, gambling results or current state, plus the entry and exit points and networks connected to them. Use that as a jurisdiction-specific input, then map the actual architecture. Do not infer scope from a domain list when a public client can call several APIs, assume multiple roles or cross an operator-supplier boundary.
Draw trust boundaries and name the owner on both sides. Include ordinary player, restricted player, customer-support, finance, content, risk, operator-admin and supplier-support roles when they exist. Record excluded assets and the reason for each exclusion. An undocumented exclusion is a blind spot, while a justified exclusion remains a visible risk decision.
Write authority and safety into the rules of engagement
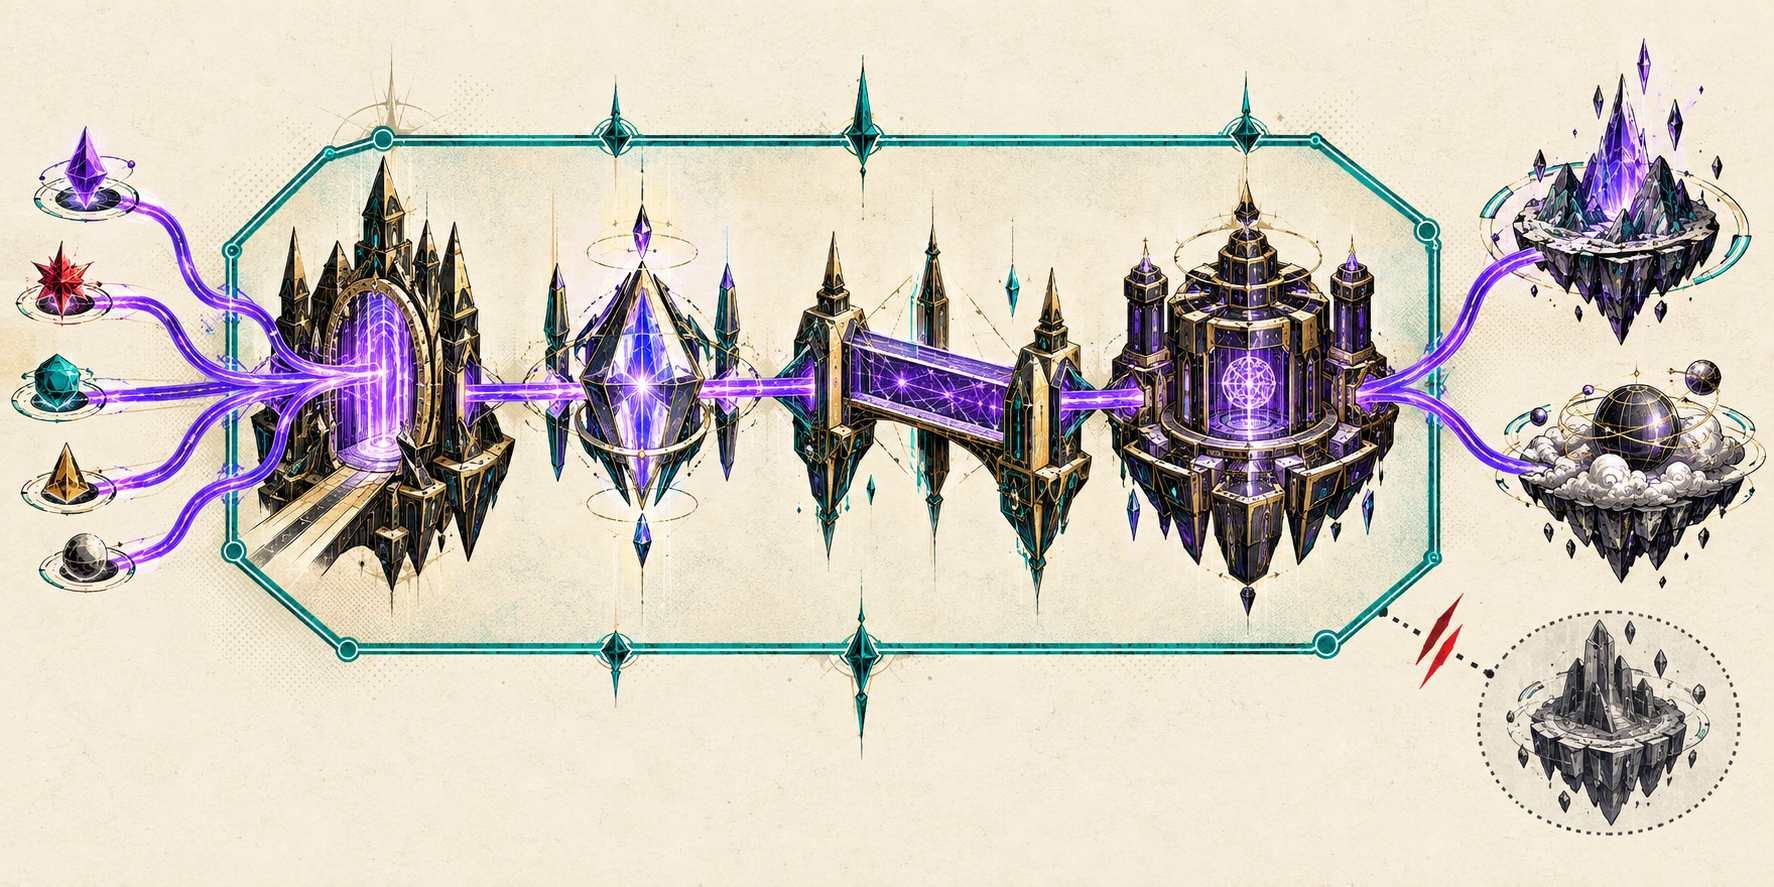
The rules of engagement should state exactly what the tester is authorized to do, when testing may occur, who can stop it and how evidence must be protected. Technical curiosity is not authorization. Give the tester written targets, dates, source addresses, approved accounts, prohibited actions, rate limits, communication channels, escalation contacts and emergency-stop conditions.
NIST SP 800-115 describes security assessments as planned activities that include testing, analysis and mitigation. It also distinguishes techniques and their limits. Turn that planning principle into an engagement record: identify the assessment owner, system owners, tester, approver and incident contact, then require a signed scope change before testing a newly discovered asset.
Protect players and production authority. Prohibit changing real balances, settling live wagers, viewing unnecessary personal data, sending player communications or degrading availability unless a separately approved scenario explicitly requires it. Define how the tester will capture, encrypt, transfer, retain and delete evidence. Provide synthetic accounts and reversible fixtures wherever they can represent the same control safely.
Choose the environment from the risk, not convenience
The test environment should reproduce the controls and trust boundaries needed for the objective while limiting harm. A staging system is useful only if identity, authorization, configuration, integration behavior and deployment artifacts are representative. A live-only control may require a tightly constrained production check, but production should not become the default because staging is incomplete.
Document every material difference between the test environment and the release candidate. Include feature flags, network policies, secrets management, third-party endpoints, data shape, rate controls, content security policy, mobile signing, API gateways and administrative roles. The iGaming non-production environment guide explains the adjacent isolation and fidelity decision; this test plan records how those differences affect security coverage.
Bind the assessment to an exact artifact and configuration. Record commit or build identity, deployed version, mobile package digest where applicable, environment identifier and test window. If the release changes after testing, classify whether the change invalidates a finding, creates new attack surface or requires focused retesting.
Derive test cases from architecture and requirements
The penetration-test plan should combine a versioned requirements baseline with product-specific abuse cases. OWASP ASVS 5.0.0 provides identifiable requirements for web application security verification. The OWASP Web Security Testing Guide supplies adaptable testing techniques and explicitly remains living guidance rather than a rigid compliance checklist.
Select the applicable ASVS requirements, record the version and map each one to the component and test evidence. Then add iGaming-specific abuse cases that a generic web list may not express: crossing player and administrator roles, replaying a wallet command, changing an object identifier across tenants, reusing an expired session, bypassing a restriction state, tampering with game or market requests, exploiting webhook trust, or moving from a supplier connection into a critical service.
Automated coverage can support reconnaissance and regression, but business-logic paths need human reasoning and authoritative domain knowledge. Test allowed behavior and forbidden behavior. A response that returns HTTP 200 may still reject the action correctly, while a blocked request may still leak sensitive state through an error, timing difference or audit trail.
Control third-party and payment boundaries explicitly
Third-party boundaries should be part of the same scope decision even when another company operates the component. The Gambling Commission’s third-party responsibility guidance says licensees remain responsible for contracted activities and need adequate due diligence, oversight and controls. That does not authorize testing a supplier without permission. It requires the operator to obtain appropriate assurance and contract a lawful test route.
Specify which party tests each interface, what evidence can be shared, how findings are coordinated and what happens when a supplier excludes a dependency. The casino game supplier security guide covers SBOM, provenance and vulnerability-handling evidence. The penetration-test pack should reference that evidence without pretending an inventory proves exploitability or a test proves the software supply chain is complete.
Apply payment requirements only to the real payment scope. The PCI Security Standards Council describes PCI DSS as a baseline for entities that store, process or transmit cardholder data, or can affect the security of that environment. Record whether the tested component is in or can affect the cardholder-data environment. Do not label an entire iGaming platform PCI compliant because one test covered one payment route.
Turn findings into release decisions and retests
The findings register should preserve the tested evidence, affected asset, attack path, preconditions, impact, severity method, owner, remediation decision and release status. A severity score helps prioritize; it does not decide whether a business-logic bypass, cross-tenant exposure or restricted-account failure is acceptable for this product.
Require reproducible evidence without storing more sensitive data than necessary. Each finding should identify the exact test version and configuration, steps sufficient for an authorized reviewer, expected and observed behavior, relevant logs and a sanitized proof. Separate confirmed vulnerabilities, observations, accepted limitations, false positives and out-of-scope discoveries.
Retest the remediation and a reasonable path around it. A validation fix may block one input while leaving an equivalent API route open. An authorization repair may protect the visible client but not the underlying service. Record the retest date, tester, artifact, result and residual risk. When a release proceeds with an accepted finding, name the accountable owner, expiry or review date and compensating controls.
The final acceptance pack should contain the architecture and scope map, rules of engagement, exact build and environment record, tester independence and competence evidence where required, test-case mapping, findings register, remediation evidence, retest results, exclusions, residual-risk decisions and secure evidence-disposal confirmation. This package does not guarantee security, certification or regulatory approval. It gives buyers and delivery teams one inspectable answer to a narrower question: what was tested, against which release, and what evidence closed the findings?
For teams commissioning or modernizing the critical services behind a casino or sportsbook, Wizards platform development can connect architecture boundaries, integration requirements and security acceptance criteria in one delivery brief.
Frequently asked questions
What should an iGaming penetration test include?
It should include a versioned scope, trust-boundary map, authorized identities and actions, rules of engagement, exact environment and build, mapped test cases, findings evidence, remediation decisions, retest results and documented exclusions.
Is a vulnerability scan the same as a penetration test?
No. A scan mainly identifies known patterns, while a penetration test uses authorized analysis to validate how weaknesses can be reached or combined in a defined scope. Both have limits and neither replaces a wider security audit.
Which iGaming systems belong in penetration-test scope?
Scope should follow sensitive data and authoritative actions across player clients, APIs, identity, wallets, game or betting services, administrator tools, data stores, networks and third-party entry points. Exclusions need an owner and reason.
Should an iGaming penetration test run in production?
Not by default. Use the environment that represents the required controls with the least risk, document every material difference and authorize any constrained production test separately with clear stop conditions.
When does a penetration-test finding need a retest?
A finding needs retesting when the release decision depends on the remediation. The retest should verify the original path, a reasonable bypass path, the exact corrected artifact and any residual risk.
Does a penetration-test report prove regulatory compliance?
No. It is one evidence source within a wider security, product and regulatory process. The applicable authority, auditor, operator and payment program determine scope, audit and approval requirements.